Project assets
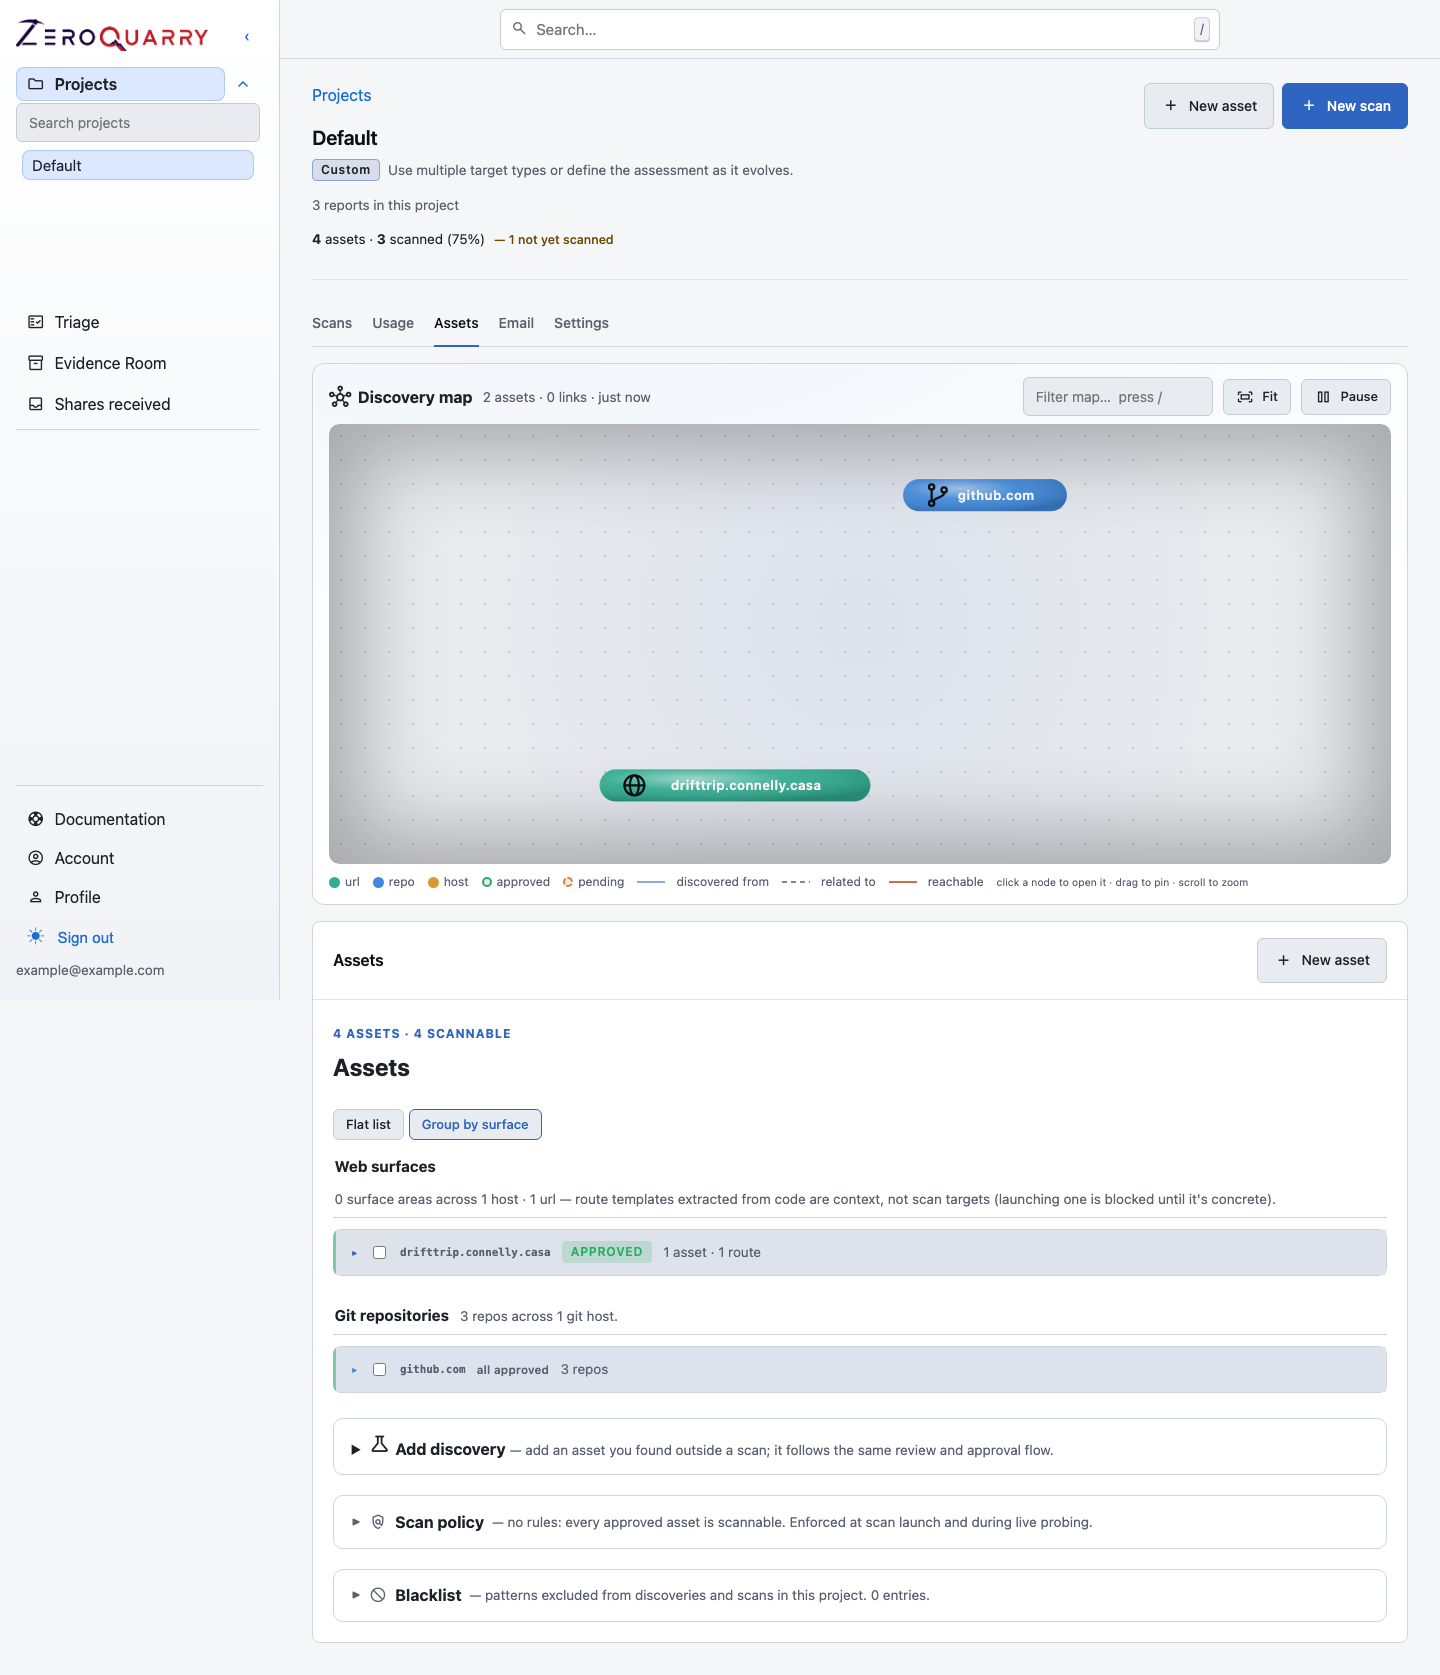
Assets are ZeroQuarry's durable record of the targets an assessment can touch. A scan points at one or more assets, and the results of every scan flow back into the same library, so a project accumulates a single growing picture of its attack surface instead of a pile of one-off scan inputs.
An asset answers what are we protecting?; a scan answers what did we ask about it this time?. That is what makes the library worth maintaining — you configure a staging login once and every later scan authenticates the same way, and an asset one scan discovered becomes a scan target for the next one.
The five kinds
| Kind | Use it for |
|---|---|
| URL | Web apps, REST APIs, GraphQL endpoints |
| Repo | Git repositories, connected GitHub repos, uploaded source |
| Host | Hostname:port services such as SMTP, databases, internal services |
| Spec | OpenAPI/Swagger documents, GraphQL schemas, MCP server definitions |
| Docs | PDFs, Word files, or a documentation repository |
Authentication lives on the asset rather than the scan, so every scan of an asset authenticates the same way. The kind is fixed at creation.
Where to go next
- What an asset is — the kinds in full, where auth lives, and which project profiles get a library.
- The asset library — the map, the table, bulk operations, scan policy, and the blacklist.
- Discovery and approval — how assets are found, labelled, grouped into surfaces, and approved.
- The asset graph — reachability, lineage, and what was never probed.
Common next steps
- Run a scan against an asset from its detail page, or start from Source code scans or Remote target scans.
- Record boundaries that must never be probed in the project's scan policy and blacklist.
- For targets that must stay inside your network, pair assets with private runners.